Email authentication: what it is and how SPF, DKIM and DMARC work
SPF, DKIM and DMARC: the three checks that decide whether your email gets delivered
Email authentication is the set of checks that lets the server receiving an email confirm that it comes from whoever claims to send it and that nobody has changed it along the way. It’s done with three records you publish in your domain’s DNS: SPF, DKIM and DMARC.
The protocol that carries email, SMTP, doesn’t check on its own who the sender is. That’s why, without authentication, anyone could send emails on behalf of your domain, and mailbox providers would distrust your sends.
Why is it important to authenticate your email?
- It protects your domain. It makes it harder to carry out spoofing and phishing that use your name to deceive your customers.
- It improves deliverability. Gmail, Outlook and Yahoo look at authentication before deciding whether an email goes to the inbox or to spam.
- It’s already a requirement. Since February 2024, Gmail and Yahoo require SPF or DKIM from all senders. Anyone who sends more than 5,000 emails a day to their users also needs SPF, DKIM and DMARC, an aligned domain, one-click unsubscribe and a low spam rate. Microsoft has applied similar requirements on Outlook.com and Hotmail since May 2025.
SPF, DKIM and DMARC: what each one checks
| Record | What it checks | DNS record type |
|---|---|---|
| SPF | That the sending server is authorized by your domain | TXT |
| DKIM | That the email carries your signature and hasn’t been modified | TXT or CNAME with the public key |
| DMARC | That SPF or DKIM pass and match your domain, and what to do if they don’t | TXT at _dmarc |
SPF (Sender Policy Framework)
It’s a record in your domain’s DNS listing the servers and IPs authorized to send on its behalf. The server receiving the email checks whether the outgoing IP is on that list. You’ll find it explained in detail in the SPF entry.
DKIM (DomainKeys Identified Mail)
It signs each email with a private key. The receiving server reads the public key in your domain’s DNS and checks the signature: if it matches, it knows the email comes from your domain and that nobody has altered it. More detail in DKIM.
DMARC (Domain-based Message Authentication, Reporting and Conformance)
It checks that the email passes SPF or DKIM and that the domain validating it matches the one the recipient sees in the “From” field. It also tells the receiving server what to do with emails that fail: nothing (p=none), send them to spam (p=quarantine) or reject them (p=reject). And it sends you reports on what it has found.
DMARC was created in 2012 by a group of companies, including PayPal, Google, Microsoft and Yahoo. It helps stop spoofing, which forges a message’s “From” field. More detail in DMARC.
How email authentication works
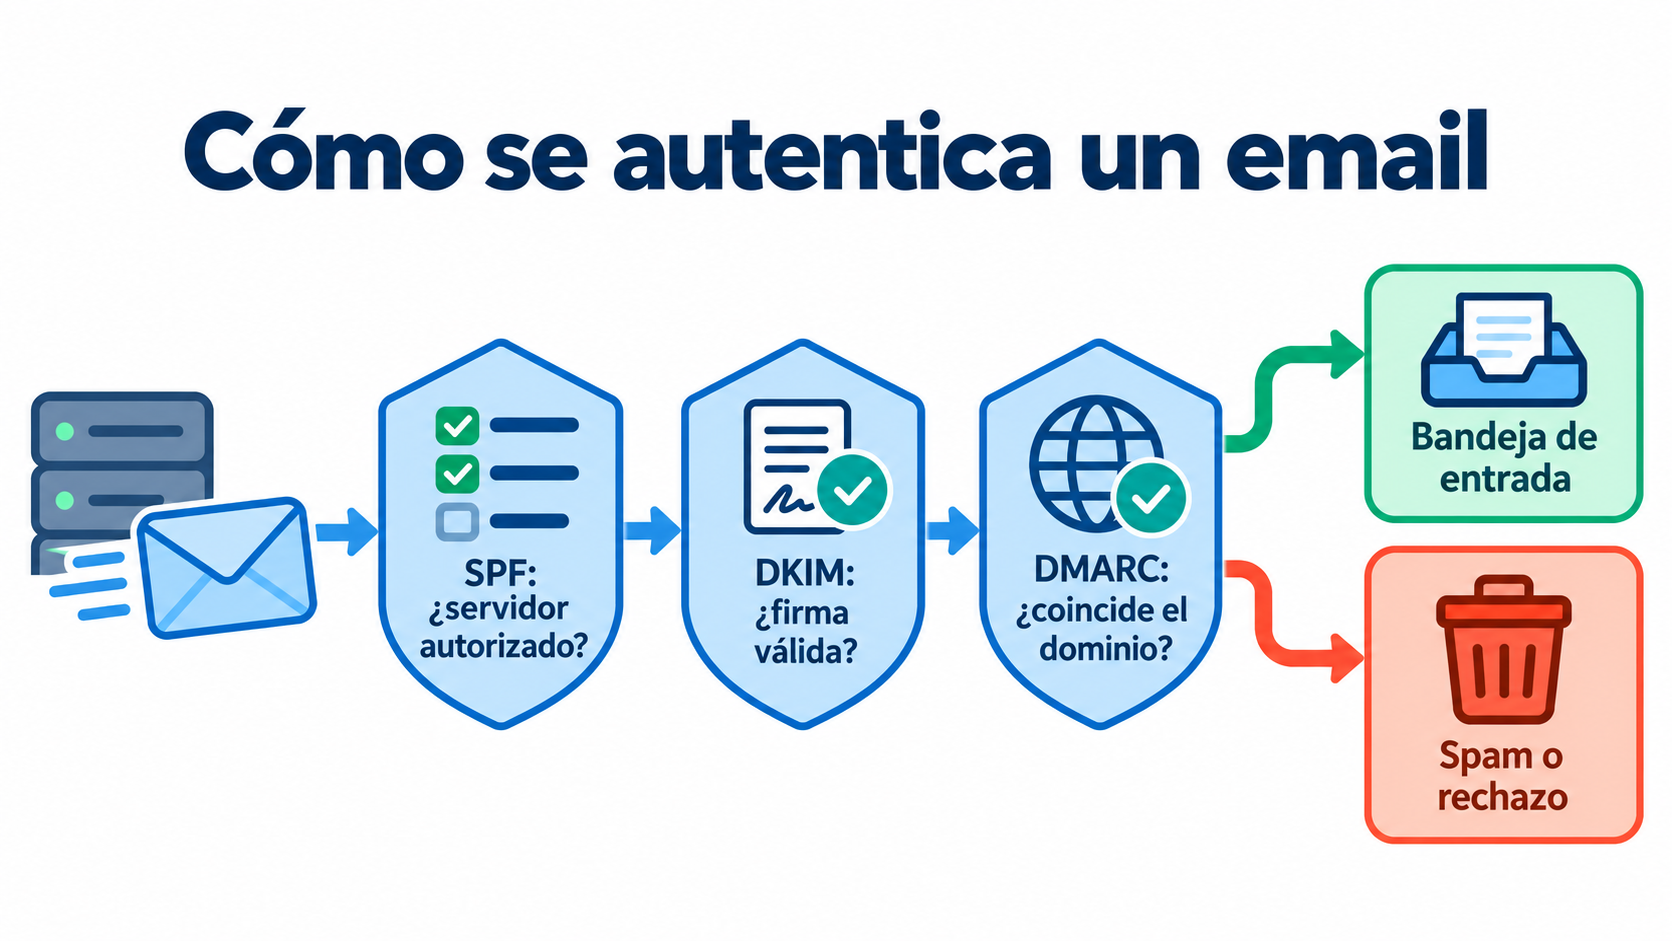
- You send the email and it goes out through your provider’s mail server or your sending platform’s.
- The server signs it with DKIM and delivers it to the recipient’s server via SMTP.
- The receiving server queries your domain’s DNS: it checks SPF, validates the DKIM signature and applies your DMARC policy.
- Then it looks at the sender reputation and IP reputation, the content and its antispam filters.
- If everything checks out, the email reaches the inbox. If it fails, it can go to spam or be rejected.
Send with your authenticated domain
Set up SPF, DKIM and DMARC on your sending domain and earn the trust of mailbox providers.
How to check whether an email is authenticated
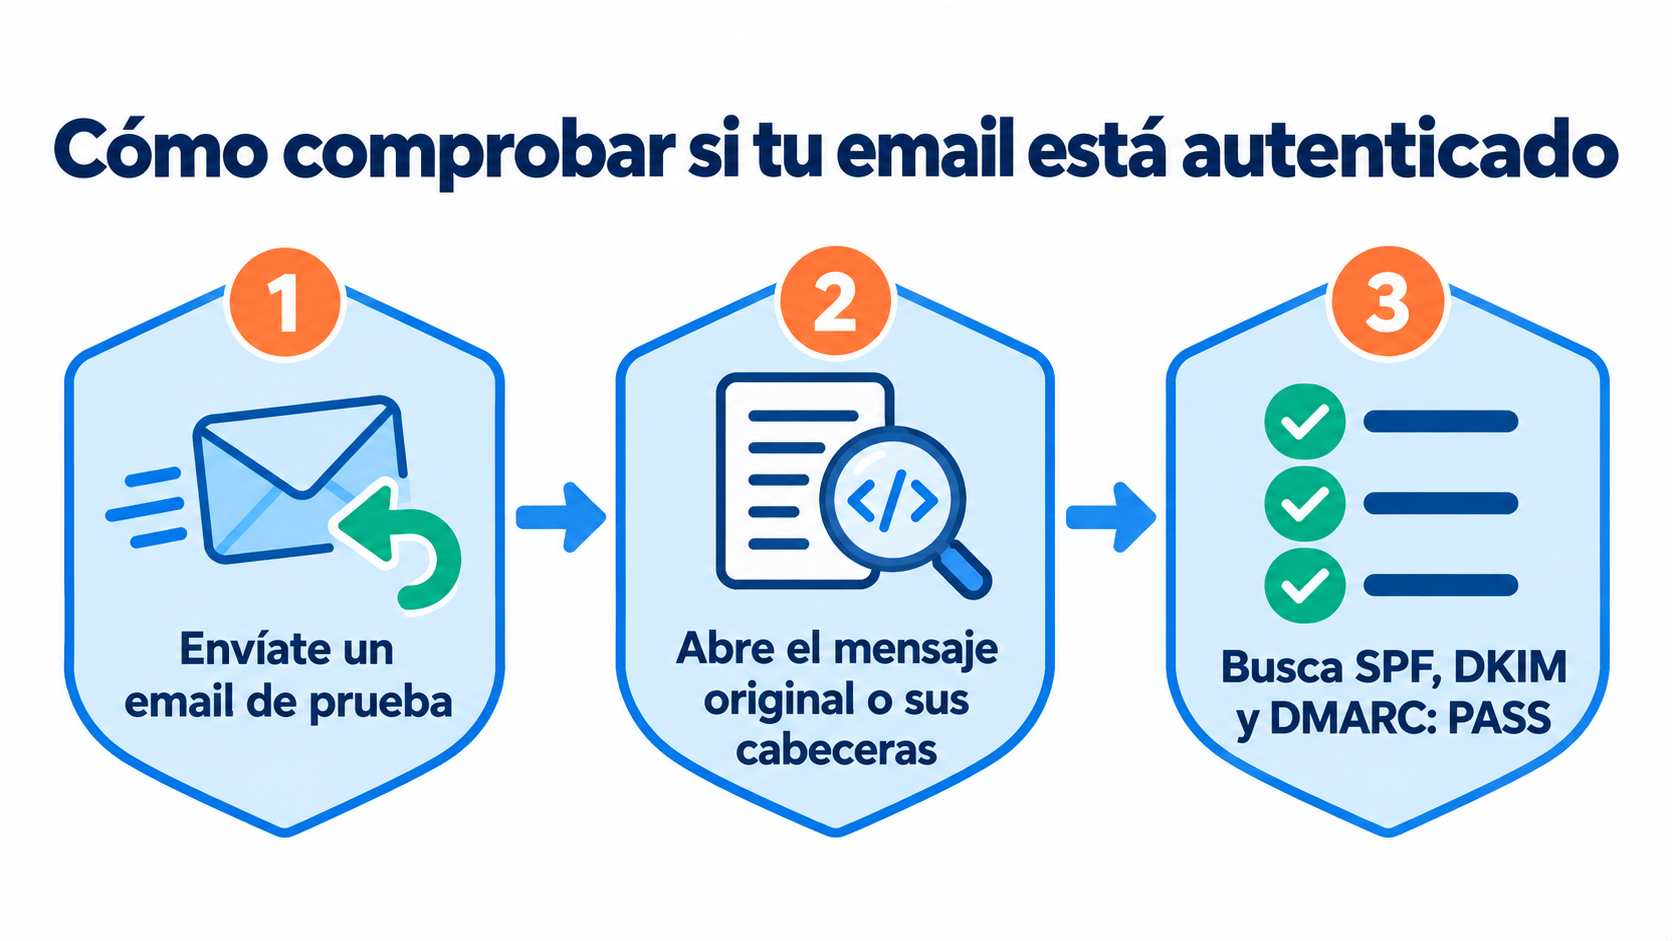
- In Gmail: open the email, click the three dots and choose “Show original”. At the top you’ll see SPF, DKIM and DMARC with the result: PASS if everything is fine.
- In Outlook: open the message properties or source and look for the “Authentication-Results” header, with spf=pass, dkim=pass and dmarc=pass.
- Before a campaign: send yourself a test email and review those results. If any of them fails, review the record in your domain’s DNS.
Common mistakes when authenticating email
- Having two SPF records on the same domain. There can only be one: if you use several services, they are combined in the same record.
- Forgetting a tool. If you send from your mailbox, your online store and your email marketing platform, all three need to be authorized.
- Setting up SPF and forgetting DKIM. With forwarding, SPF can fail; the DKIM signature remains valid.
- Staying at p=none forever or jumping straight to p=reject. The sensible approach is to start with “none”, read the reports and tighten the policy gradually.
- Not checking it afterwards. A change of provider or DNS can break authentication without you noticing.
How Mailrelay helps you
In Mailrelay you authenticate your domain with four DNS records: SPF, custom domain, DKIM and DMARC. You’ll find the exact values and step-by-step instructions in the tutorial How to configure SPF, DKIM, DMARC and custom domain in Mailrelay.
With your domain authenticated, your campaigns go out with your own domain. All subscriptions go through double opt-in, unsubscribes are handled automatically and addresses with a hard bounce are never sent to again: that way you also protect your sender reputation.
Reach the inbox, not spam
Mailrelay works with double opt-in and guides you through authenticating your domain.
Frequently asked questions about email authentication
Is email authentication mandatory?
No law requires it, but Gmail, Yahoo and Microsoft ask for it to deliver your emails normally, especially if you send a lot. Without authentication, you’ll usually end up in spam.
Do I need SPF, DKIM and DMARC at the same time?
It’s recommended. If you send more than 5,000 emails a day to Gmail, Yahoo or Outlook, all three are mandatory.
How long do DNS changes take to apply?
Usually a few hours, although they can take up to 48 hours to propagate.
Is it the same as two-step verification or an authenticator app?
No. Two-step verification protects access to your email account with a one-time code (we explain it in OTP). Email authentication proves that the emails you send really come from your domain.
How do I know if someone is spoofing my domain?
With DMARC reports: they list the servers sending on behalf of your domain, both authorized and unauthorized.